Firewall Management basados en el host
Enforce Windows Firewall rules across every workstation from the console you already use.
Why Host-based Firewall Management
Without central policy, each workstation runs its own rules. One gap is enough.
Each endpoint firewall has its own set of rules, creating work for admins and weak spots for attackers.
Manage Windows Firewall from the console and agent you already use. Ready-made rulesets get you up and running on day one.
Capacidades
Only authorized traffic gets in or out, shrinking the attack surface and helping contain threats.
Start with 371 rules across 37 built-in rulesets covering common Windows needs, so you don't have to write the basics yourself.
Apply stricter rules when a workstation connects to an unsecured network, and allow more flexibility on the networks you manage yourself.
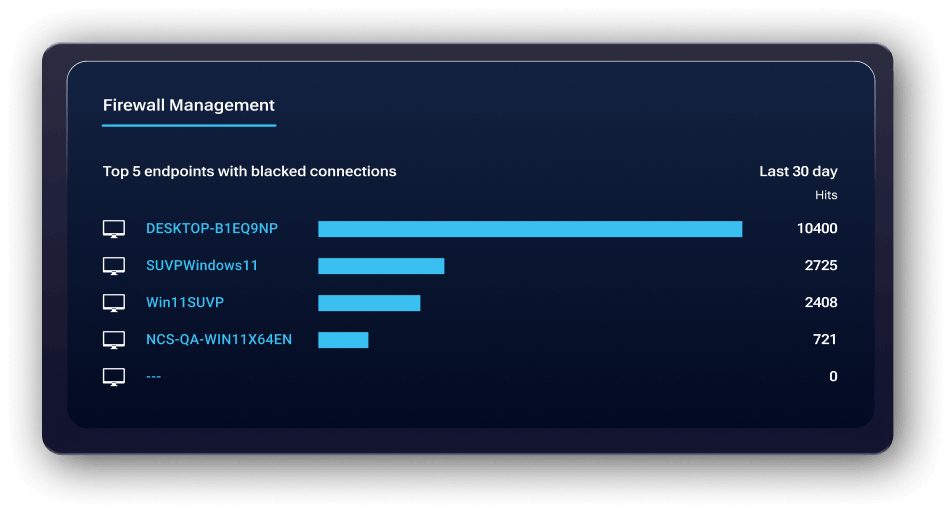
The Activity tab shows network traffic, blocked connections, and which rules were enforced, so you can troubleshoot without guessing.
The firewall runs in the agent you already have, alongside EDR and patching.
Without Host-based Firewall Management
With Host-based Firewall Management
See rules, policies, and blocked connections in one place.
De una misma infraestructura están surgiendo dos ecosistemas de IA: uno legítimo y otro delictivo.
¿Está preparada tu organización?