DNS Filtering
Block malicious websites and enforce policies across every managed endpoint, from the console you already use.
Why DNS Filtering
DNS Filtering protects every user, wherever they work.
Every phishing link, malware download, and C2 callback starts with a DNS lookup, but your firewall only sees them when users are in the office or on the VPN.
DNS Filtering checks every lookup right on the endpoint and blocks threats before they connect, on or off the network, protecting remote users even without a VPN.
Capabilities
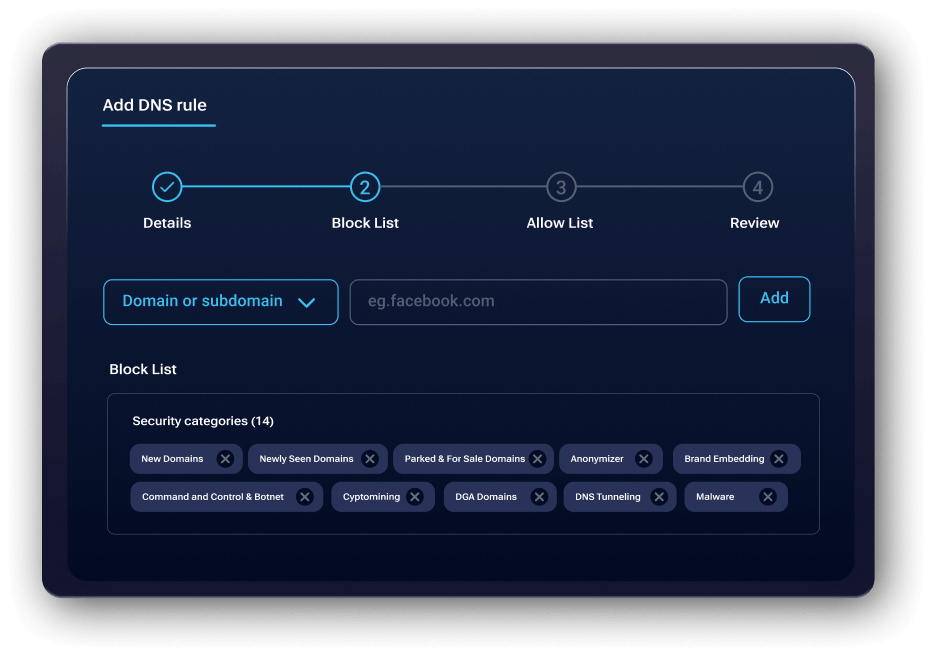
Enforces category-level browsing policies across your fleet from a single policy, covering adult content, gambling, social media, and gaming.
Blocks malware, phishing, C2, botnets, cryptomining, and more at the DNS layer, before the endpoint makes a connection.
Choose Basic, Balanced, or Strict: three ready-made protection templates that cover most environments without touching individual category settings.
Blocks content categories by policy, adult content, gambling, and more. Logs 90 days of DNS activity, exportable for audits.
Purpose-built DNS security, built into the agent you already deploy.
Without DNS Filtering
With DNS Filtering
For managed service providers
No new agents, no new provisioning. Protect any client in minutes.
DNS Filtering is already part of ThreatDown, no separate agent or console needed. Deploy it to any client in minutes from the console you already use.
Set DNS policies and blocked-site messages for every client from one console. Global exclusions push across your entire client base without opening individual sites.
See DNS Filtering in action across your endpoints.
Two AI ecosystems are growing from the same infrastructure: one legitimate, one criminal.
Is your organization prepared?